Security
Trusted by enterprises
We strive to meet the highest level of security certification across borders and industries. Our compliance is managed by Oneleet and our audit partners.
Trusted by 400+ revenue teams to replace 6sense & Demandbase




SOC 2 Type 1
We’re in the midst of our SOC 2 Type 2 audit.
GDPR
We’re GDPR compliant. Ask us for our DPA.
CCPA
We’re CCPA compliant. Ask us for our DPA.
CASL
We’re CASL compliant. Ask us for our DPA.
PIPEDA
We’re PIPEDA compliant. Ask us for our DPA.
LGPD
We’re LGPD compliant. Ask us for our DPA.
POPIA
We’re POPIA compliant. Ask us for our DPA.
PDPA
We’re PDPA compliant. Ask us for our DPA.
Security program
Built for your security review
The controls behind Vector, monitored continuously by Oneleet. Request our documents in the trust center.
Encrypted everywhere
Data is encrypted at rest and in transit, and on every employee device.
Access kept tight
MFA is required for critical services, and employee access is reviewed regularly.
Tested from the outside
An independent penetration test in the last 12 months, with every finding remediated.
Backed up and recoverable
Automated, isolated backups and a disaster recovery plan we test.
Logged and monitored
Audit logs are collected, infrastructure changes are logged, and the network is monitored.
Patched and scanned
Infrastructure is scanned and software patched automatically, and vulnerabilities are remediated.
How identification works
Drive GTM value, with compliant peace of mind
We understand the challenging role of security and legal professionals in an ever-shifting privacy landscape. We commit to making sure our customers understand exactly how Vector works.
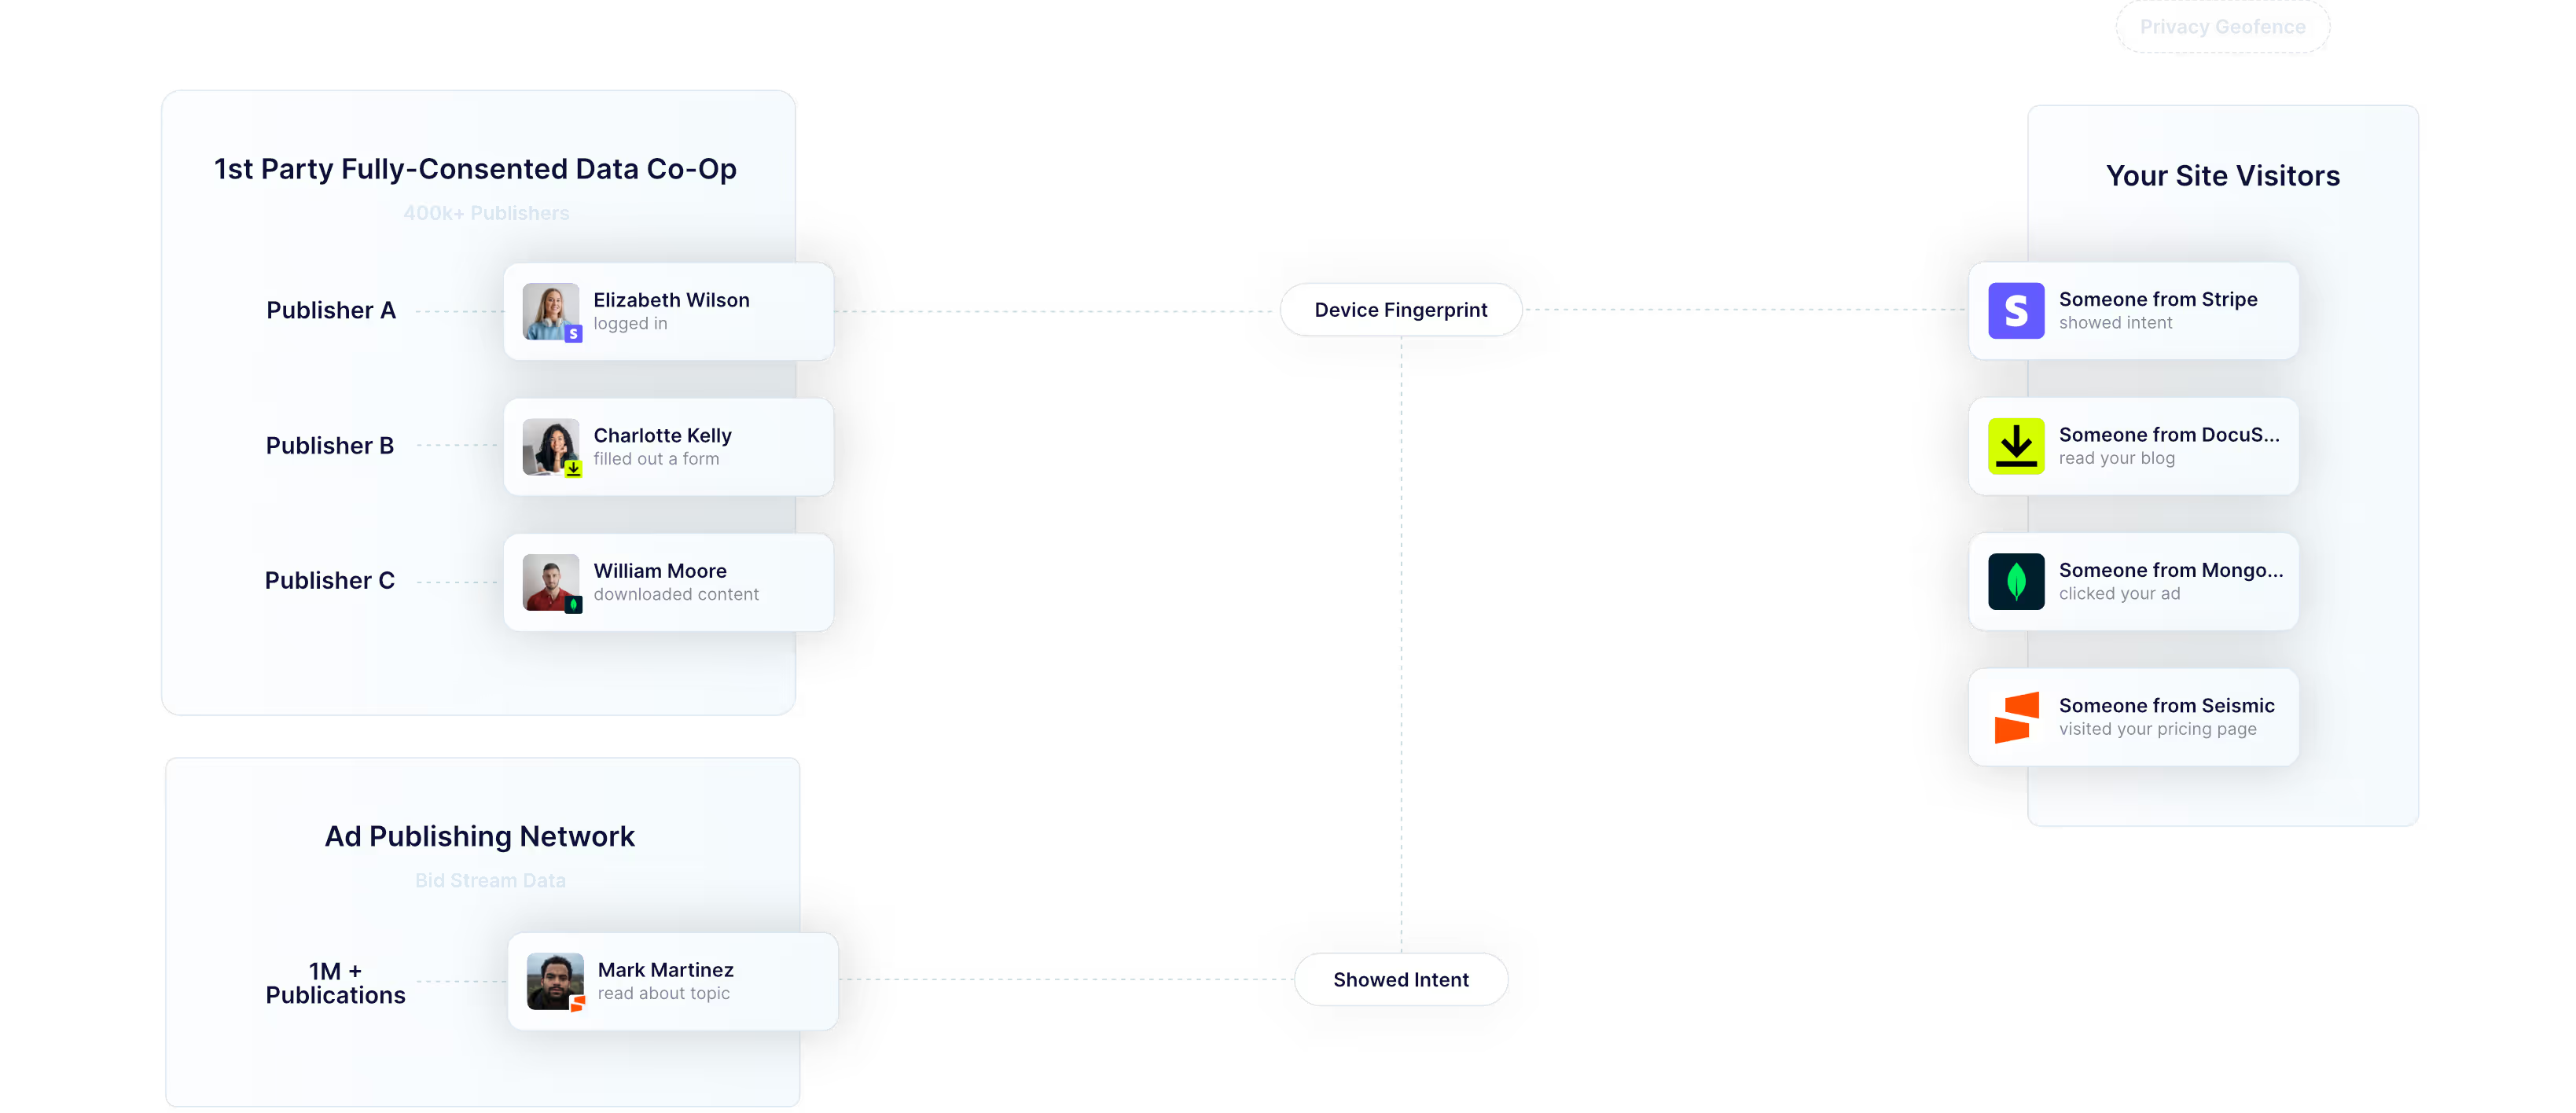
Vector has a proprietary network of publishers who properly disclose, collect, and share their first-party data: namely, hashed emails (HEMs) and associated device fingerprint information.
When a visitor lands on your site, we only look at device fingerprints to determine if an identity can be found in our pre-existing, compliantly sourced identity graph. We geofence our technology to jurisdictions with implied opt-in, and you can further gate Vector behind a consent management platform (CMP).
You do not become a contributing member of the data co-op.
We require our customers to update their privacy policy and CMP, where applicable.
Security, answered
Common questions about security, trust, and compliance.
Vector is geofenced to only operate in the United States. That doesn’t remove your responsibility in places with tighter regulations, but it drastically reduces risk exposure to subjects in those jurisdictions.
Send the request to security@vector.co.
Yes, in two ways. On your end, you can install Vector within a container or consent management platform (CMP) that disables its functionality. Individuals can also send deletion requests to security@vector.co.
We require customers to update their privacy policy and CMP, where applicable. While Vector warrants the rights for the data we surface, customers are solely responsible for implementing Vector’s technology in a compliant manner. Always consult your legal, privacy, and security team, but unless you already have this covered, consider a clause to the effect of: "By accessing or logging into our website, our online data partners or vendors may use cookies and related technologies to connect your activities with other personal information they or others may hold about you, such as your email or online profiles. We, or our service providers, might then send you communications and marketing materials to these emails or profiles. To opt out of these communications, please email us at security@vector.co."
Yes. Vector already geofences to jurisdictions with implied opt-in, and you can raise your security posture with explicit opt-in by placing Vector inside a container or CMP.
Yes, Vector only fires in the United States. To do so, Vector technically fires globally to calculate a visitor’s IP address. This data collection is incidental and for privacy purposes, which means no "establishment" is created for "the effective and real exercise of activities through stable arrangements".
That’s possible, and it would make Vector (and you) responsible for protecting that individual’s citizenship rights. That’s why Vector builds none of its identity graph with information from outside the US: we don’t collect or purchase any non-US data, so a device fingerprint can’t be enriched to an individual from a foreign jurisdiction.
Request access in our trust center at trust.vector.co, where you’ll also find our latest penetration test, or email security@vector.co.
Yes. Email security@vector.co and we’ll send it over.
Yes. Data is encrypted in transit and at rest, and on every employee device.
Yes. An independent penetration test ran in Q4 2025, and its findings were remediated. Request the report in our trust center.
Bring your security questionnaire
We’ll walk your team through how Vector works, the controls behind it, and our reports.